Your SOC, rewired for AI-driven attacks.
The AI SOC with forensic depth.
Trusted by the world’s most targeted enterprises.




AI-driven attacks hide where your SOC isn’t looking
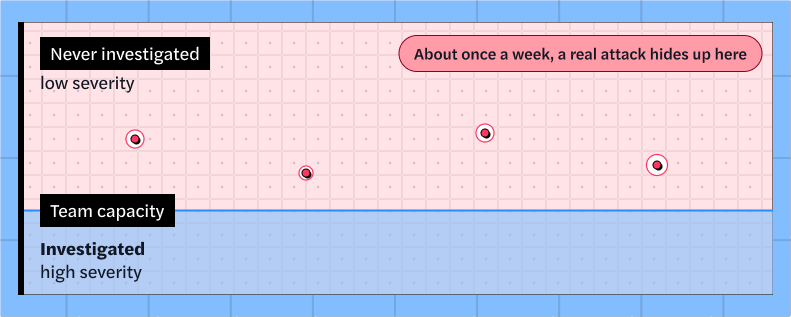
AI-driven attackers log in with valid credentials and use your own admin tools, hiding in low-severity alerts at machine speed and scale. Human-paced SOCs and MDRs work by severity, so real attacks sit at the bottom of the queue.
Why Intezer: forensics fused with AI
AI-planned investigations, proven by deterministic forensics:
verdicts that hold up, at a flat per-endpoint cost.
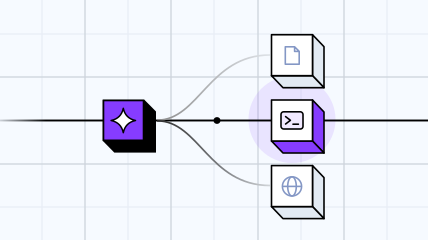
AI reasoning that
steers the investigation
The AI plans each investigation, decides which artifacts, logs and context matter, and keeps asking the next question as findings come in, so nothing relevant is missed.
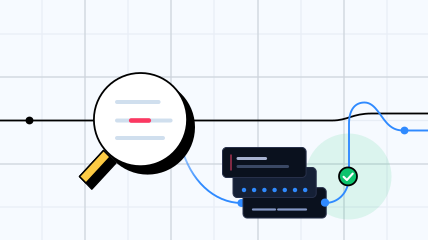
Forensic depth, down to the code
Memory analysis, reverse engineering, sandboxing and threat intelligence turn an alert’s artifacts into facts for the AI to reason over, so the same file, memory or code yields the same facts every time.
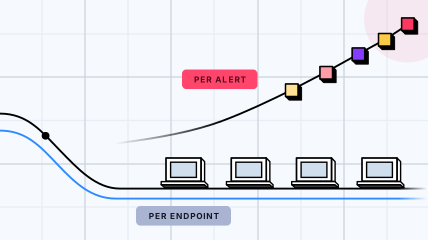
Predictable cost as you grow
Deterministic analysis does the heavy lifting, so AI reasoning is spent only where it adds value, at a flat per-endpoint cost regardless of alert volume or tokens.
The complete AI SOC
Triage, investigation, response and detection engineering in one platform, grounded in your organizational context.
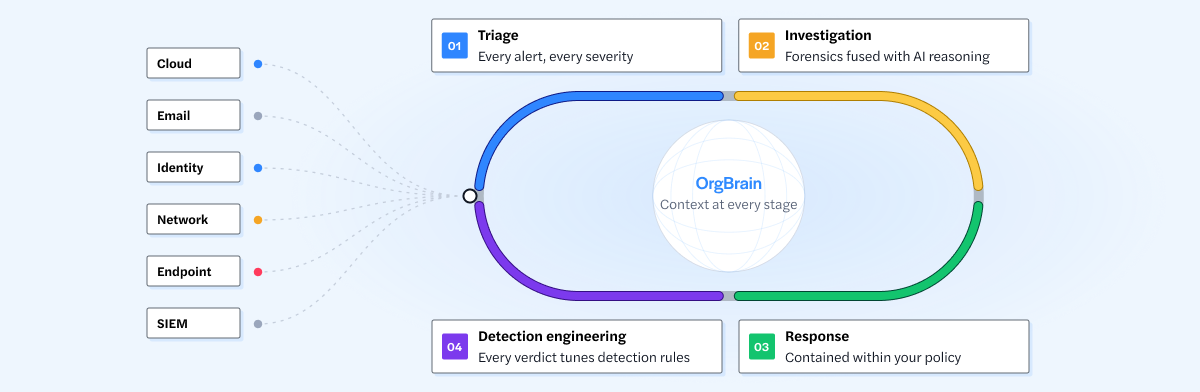
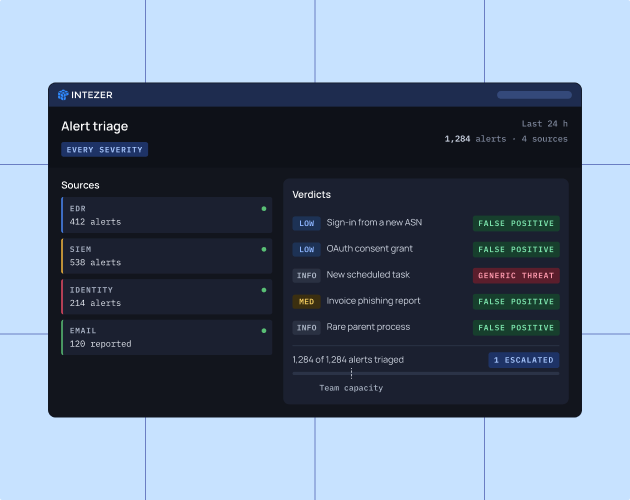
Find the threats hiding in the noise
Intezer investigates every alert at any volume, and per-endpoint pricing keeps full coverage affordable.
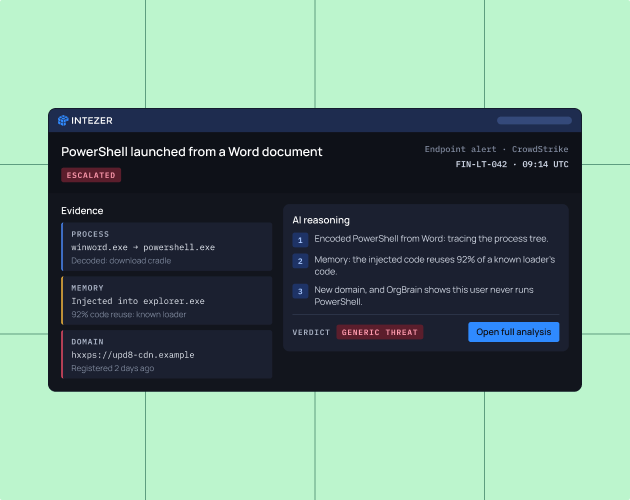
Every verdict comes with proof
Endpoint artifacts are analyzed down to the code, and AI reasoning weighs the facts against threat intel and context.
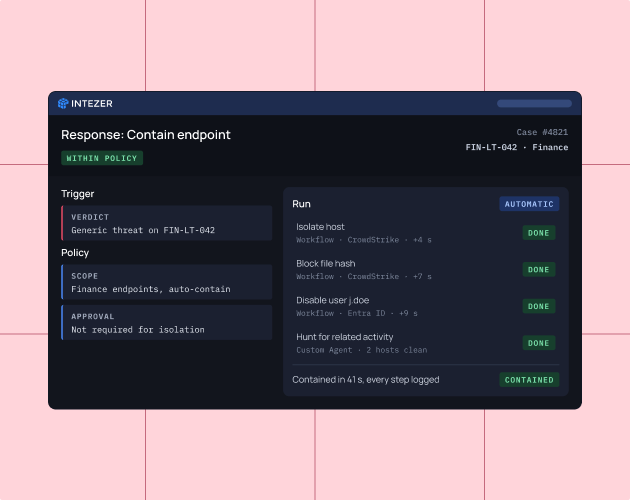
Stop threats before they spread
Workflows contain confirmed threats within your security policies, while Custom Agents handle follow-up actions, such as hunting for related activity.
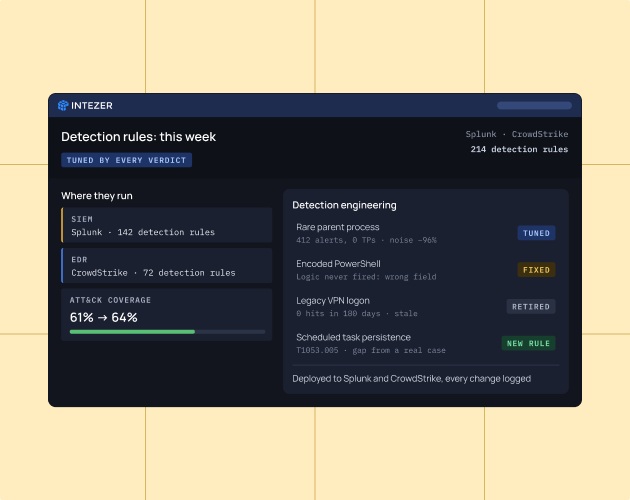
Continuously sharpened, fewer blind spots
Verdicts show which detection rules catch real threats. Intezer continuously tunes them in your SIEM and EDR and closes ATT&CK gaps.
Fewer false alarms, every decision on record
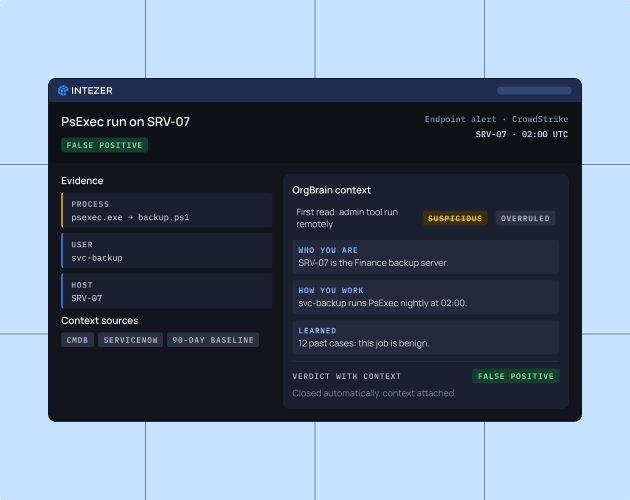
OrgBrain applies what it learns from past cases and tickets, and every verdict keeps its evidence, reasoning and actions on record.
What we deliver
98%
Verdict accuracy, with evidence attached
<2%
Of alerts escalated to your team
~1 min
To reach a verdict
Predictable pricing
Per endpoint, not per alert or token
Why security leaders trust Intezer with every alert
Security teams share what changed once Intezer started handling their alerts.






Integrations built for investigation
Intezer connects to your security platforms, ingesting alerts and enriching every investigation with the context it needs across identity, asset, cloud, log tools and more.




Latest from Intezer
See all resources
2026 AI SOC Report for CISOs
What 25M+ alerts reveal about the threats hiding in low-severity noise.
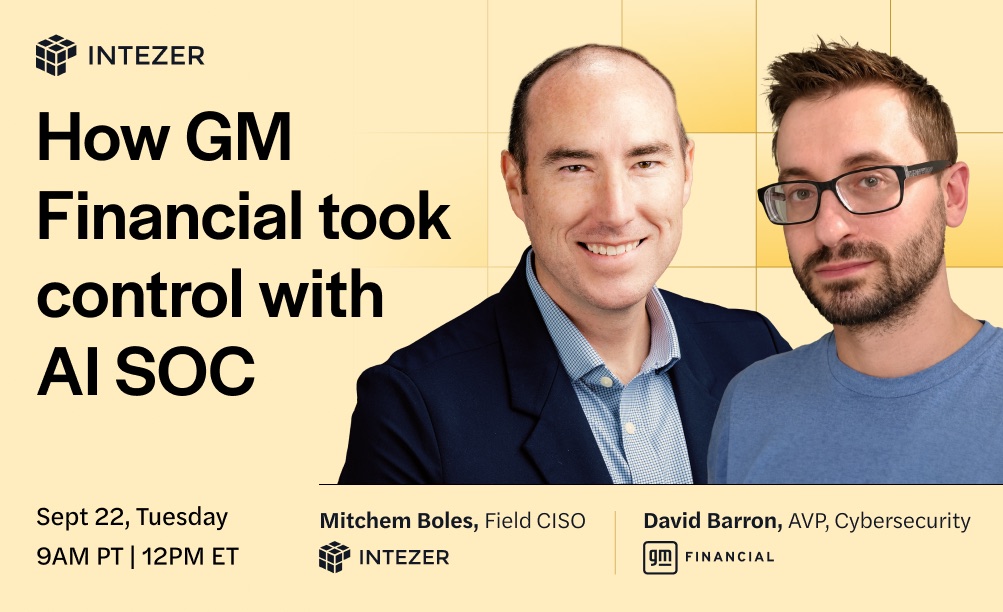
AI SOC Live, Episode 8: How GM Financial took control with AI SOC
GM Financial’s David Barron on catching early attack signals in low-severity alerts.

100 CISOs ranked their 2027 priorities for a16z: AI SOC takes #1
What the a16z survey says about where security budgets go next.

See every alert investigated
Bring your noisiest alert source and we’ll show you how every alert is investigated, the evidence behind each verdict, and how threats are contained within your policy.